Your internal context layer, and what RAG and MCP actually are
Two bits of plumbing with unhelpful names. RAG is how a tool looks things up in your documents before it answers. MCP is a standard way for a tool to plug into your systems. Most businesses need the first, some need the second, and neither one is a strategy.
Think of a new starter
Imagine a capable new starter. On day one they know a great deal in general and nothing about your business. Two things make them useful.
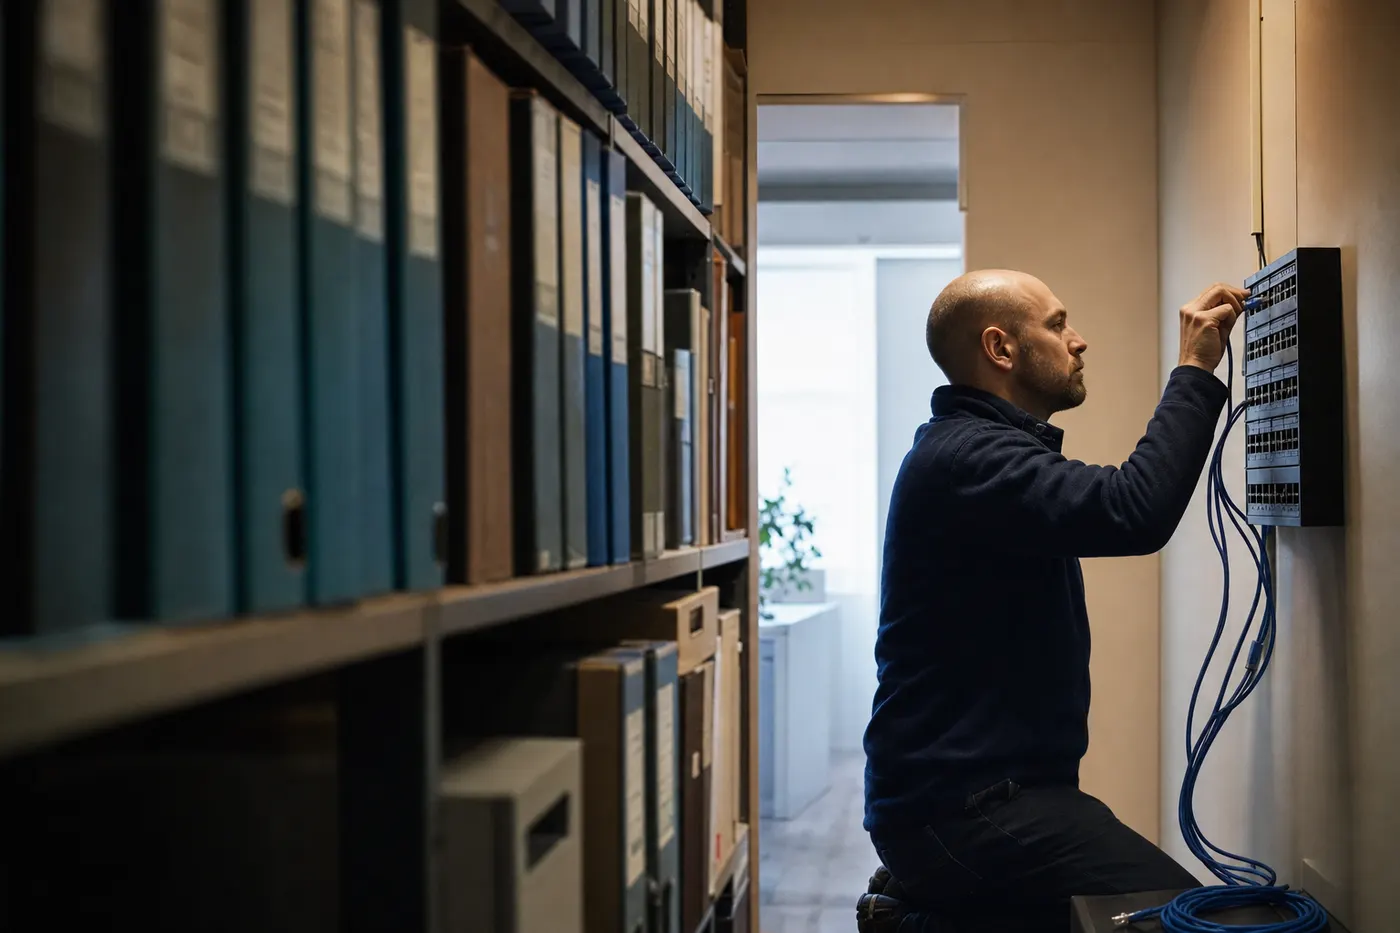
The first is a filing cabinet they're allowed to open – your procedures, your price list, your past proposals, the notes from last month's customer meeting. When you ask them a question, they go to the cabinet, find the right pages, read them and answer. That's RAG. The model is the new starter, the cabinet is your material, and the looking-up is the retrieval.
The second is the way their tools plug into the office: the phone system, the CRM, the calendar. If every new starter needed a bespoke cable made for each system, nobody would bother. A standard plug means any tool connects to any system the same way, with the permissions set at the socket. That's what MCP is trying to be.
How RAG works
Your documents get split into passages and indexed. When a question comes in, the tool searches the index for the passages most likely to be relevant, hands those to the model along with the question, and the model writes an answer from them – ideally saying which passages it used. The model's memory isn't the source. Your material is.
So when a RAG answer is wrong, it's usually the cabinet, not the clerk. The document was never added, two versions are in there and it found the old one, the passage it found was about something else with similar words, or there's so much material the useful page got crowded out. Frustrating answers are usually context goes into this. The fix is nearly always tidying the library, not changing the model.
What MCP does
MCP is a published standard for how a tool asks a system "what can you do?" and "do this", and how the system answers. A CRM that offers an MCP connection can be used by any tool that speaks it, and the permissions get set once, at the CRM end. It's the difference between a wall of custom adapters and a row of standard sockets.
It doesn't make the tool any smarter. It makes connecting cheaper, more consistent, and easier to see and switch off, which is exactly what the access controls need. It's also young – not every system offers it yet, and the quality of a connection depends on what the system behind it chooses to expose.
Standard connector or the vendor's own features
Most assistant vendors give you their own ways to feed the tool context: a project with files attached, a built-in connector to a drive, a "knowledge" feature. They're easier to set up and they're tied to that vendor. A standard connector takes more setting up and moves with you when you go.
| Vendor's own context | Standard connector (MCP or similar) | |
|---|---|---|
| Setup | Minutes. | Hours to days, once per system. |
| Who can use it | That vendor's tools. | Any tool that speaks the standard. |
| Permissions | In the vendor's settings. | At your system, where IT can see them. |
| If you change vendor | Rebuild it. | Keep it. |
| Right for | A team's personal assistants, a small library. | Agents, shared systems, anything you want to keep when you leave. |
Our view, for what it's worth: use the vendor's own features for personal assistants and small libraries, because they're quick and being wrong costs you little. Use standard connectors for anything an agent depends on or anything that touches the CRM, because you'll change vendor one day.
Managing the context layer day to day
Five habits, and none of them are technical:
- One library, in the internal ring, where the material the tools may read actually lives. Not 6 drives.
- Owners and review dates on the material, so old versions get removed rather than discovered.
- The rings decide what may be connected, and the systems owner connects it.
- Standard plugs for shared systems, with the permissions set at the system end.
- A log of what each tool read and did, for the owner's sample check.